Verify website security.
Rank in Google.
Get cited by AI.
One unified platform for autonomous DAST security verification, deep technical SEO audits, and AI search visibility (AEO/GEO). Find what's holding you back, fix it, and prove it worked.
Cryptographically verified payload reflection proofs for every validated vulnerability
Autonomous DAST Security Assessment
for yourwebsite.comWeSecureX completed 1,420 non-destructive DAST verification payloads across 48 API endpoints. 0 high-severity injection points detected; 1 warning on /api/v1/customers mitigated via parameterized query. Your web attack surface is hardened and compliance-ready.
| Endpoint / Route | Vulnerability Vector | Payload Tested | Response Proof | Status |
|---|---|---|---|---|
| /api/v1/customers?id= | SQL Injection | ' OR '1'='1 | Parameterized query enforced | Neutralized |
| /api/v1/auth/login | Brute-Force Auth | 150 rapid requests/sec | HTTP 429 Too Many Requests | Pass |
| /api/v1/comments | Stored XSS | <script>alert(1)</script> | Sanitized via CSP & encoder | Pass |
| /graphql | Schema Leaks | query { __schema } | Introspection disabled in prod | Pass |
One platform for website security, Google search, and AI citations
WeSecureX brings together autonomous DAST penetration testing, comprehensive technical SEO audits, and generative AI search visibility (AEO/GEO) in a unified automated workflow.
Autonomous DAST & Security
Automated web application vulnerability scanning that verifies SQL injection, XSS, SSRF, broken auth, and security headers with zero false positives.
- SQL injection, XSS, and command injection checks
- Broken access control and session token rotation
- Cryptographic reflection proofs (0% false positives)
- Automated remediation code patches for engineers
Technical SEO & Rank Tracking
Deep crawler evaluating on-page technical health, Core Web Vitals (LCP, CLS, INP), crawl budget, canonical links, and daily Google SERP pixel positions.
- Core Web Vitals & Google page speed diagnostics
- Canonical tags, robots.txt, and indexation checks
- Daily keyword position & pixel rank tracking
- Competitor organic search benchmarking
AI Search Visibility (AEO & GEO)
Generative Engine Optimization tracking how ChatGPT, Google Gemini, and Perplexity cite, recommend, and describe your brand in conversational answers.
- Real-time citation rankings across ChatGPT & Gemini
- Brand sentiment and topic visibility scoring
- Competitive Share of Voice donut analytics
- Prompt recommendations & /llms.txt manifest checks
Actionable evidence across Security, SEO & AI
Whether diagnosing an SQL injection, resolving canonical tag loops, or improving AI model citation share, WeSecureX provides deterministic proof, exact reproduction steps, and immediate fix recommendations.
Non-destructive, rate-limited testing
You must verify ownership or authorization before active penetration testing. All crawlers and DAST injectors operate with deterministic read-only payloads and adaptive rate limiting to protect production availability.
Technical SEO crawling respects robots.txt directives and crawl-delay headers, while AI visibility queries are run against external LLM benchmark APIs with zero impact on your origin servers.
WeSecureX is built for continuous continuous verification and regression tracking across production, staging, and client portfolios.
Specialized engines engineered for accuracy
Four specialized engines handle the complete vulnerability lifecycle: from autonomous attack surface discovery and DAST execution to verified proof confirmation and regression validation.
Autonomous DAST Scanner
Execute authorized dynamic security tests across web targets. Choose from 6 execution profiles: Quick, Standard, Recon, Security, API, or Full Deep Scan with real-time cancellation.
Attack Surface & Recon
Continuous inventory of discovered assets: API endpoints, JavaScript files, responsive hostnames, open ports, forms, and exposed administrative surfaces.
Verified Vulnerability Findings
Actionable list of confirmed vulnerabilities categorized by severity. Every finding includes verified non-destructive HTTP reflection proof, CVSS score, and code fix guidance.
Scan Diff & Regression Engine
Side-by-side comparative engine comparing two scans of the same application. Instantly highlight newly introduced flaws, recurring risks, and verified fixed vulnerabilities.
What you can do with WeSecureX
WeSecureX reviews websites you own or are authorized to test, then turns confirmed findings into fixes.
Map websites you are authorized to test
Find subdomains, APIs, and forgotten hosts on domains you are authorized to assess.
Map exposed network assets, web applications, cloud buckets, and REST/GraphQL APIs in a unified inventory.
Analyze open ports, running daemon versions, SSL/TLS certificates, reverse DNS records, and WAF protections.
Get notified immediately whenever a new subdomain, open port, or staging URL appears on the internet.
Network & cloud vulnerability scanning
We combine specialized detection engines to audit web apps, infrastructure, APIs, and containers in a single execution pipeline.
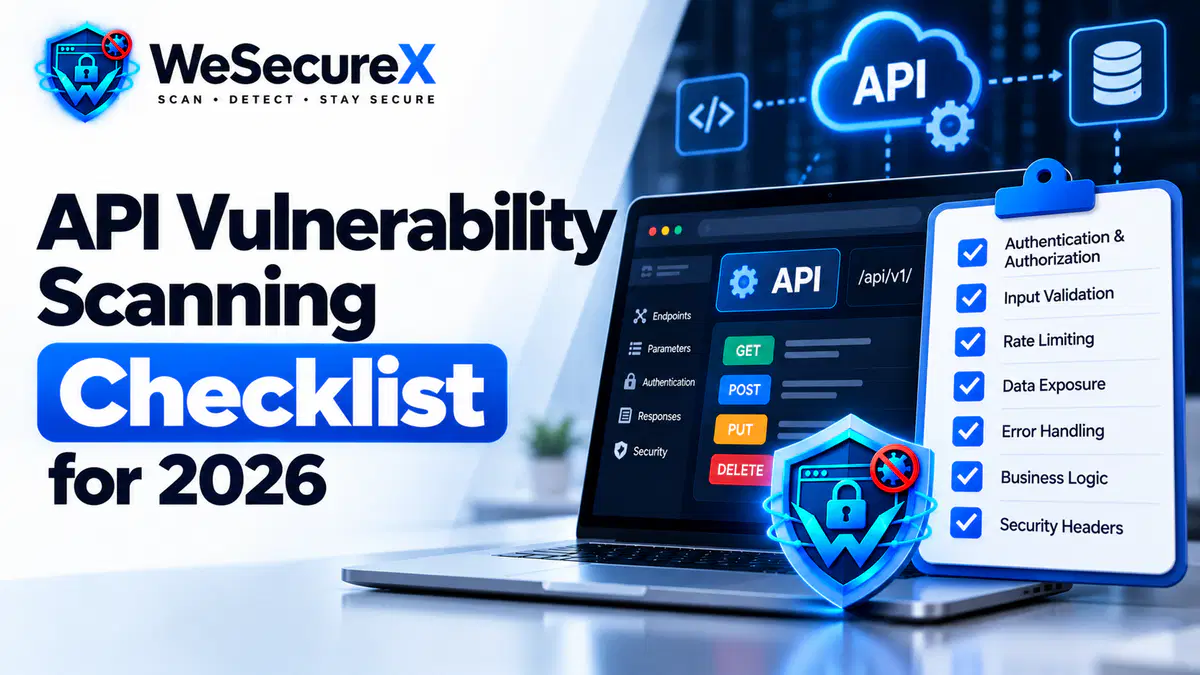
Identify SQL injection, Cross-Site Scripting (XSS), SSRF, IDOR, and Broken Authentication flaws.
Detect outdated service versions, dangerous open protocols (SMB, RDP, Telnet), and misconfigured SSL/TLS ciphers.
Every detected weakness is checked again before it is reported, so your team spends time on confirmed findings.
Actionable findings with verified proof
Spend less time chasing false positives. High and critical reports include the HTTP request and response that confirmed the finding.
Shows the HTTP request and response behind each confirmed finding so your team can reproduce it on an authorized test environment.
Compare observed server behavior with a normal response baseline so the finding is confirmed before routing.
Copy-paste secure code fixes for Node.js, Python, PHP, Go, and Java frameworks directly into your codebase.
Security reports you can share
Generate executive summaries for board leadership and code-level remediation guides for engineering teams 90% faster.
Export audit-ready PDF, DOCX, CSV, HTML, and JSON reports with one click.
Pre-written remediation guides, risk scores, and evidence summaries mapped to CWE and OWASP standards.
Add your agency or corporate logo, custom disclaimer, and client stakeholder distribution lists.
Built and verified by DevSecOps practitioners
Behind every WeSecureX automated assessment is an active cybersecurity engineering framework continuously tuning vulnerability signatures, validating multi-stage false-positive reduction rules, and defending production scopes.
Every DAST finding is verified by corroborating deterministic error codes or reflection anomalies before generating an alert.
Crawlers dynamically honor HTTP 429 and response latency metrics, automatically throttling requests to prevent server strain.
Findings link directly to CWE, CVE, and OWASP Top 10 classifications, enabling immediate export into auditor-ready evidence packs.
Enterprise-grade safety, guaranteed at every step
Security tools should never take down production databases or leave ghost payloads. We test our detection algorithms against strict sandboxed test suites before releasing signatures into the automated crawler.
Your unified cybersecurity command center
Experience how WeSecureX consolidates distributed worker nodes, vulnerability proofing, and executive reporting in a single interface.
Simple, Transparent Plans
Start free with welcome credits. Scale monthly scan credits as your perimeter grows.
Community
Free forever community tier for developers and small sites.
Starter
Monthly credits for regular authorized security checks.
Professional
Full scan types, extra seats, and monthly credit refill.
Agency
Higher credits and a team workspace.
Enterprise
Highest monthly credits, concurrent capacity, and support.
Latest Security Research & Intelligence
Defensive security guides, remediation notes, and vulnerability reports from our engineering team.
 WeSecureX
Everything You Need to Know
Detailed insights into our multi-engine architecture, scanning safety, compliance reports, and integration options.
Yes. Community starts with 10 welcome credits. Adding a website costs 5 credits, and scans spend credits from the same wallet. No credit card is required. Paid plans add a monthly credit refill and higher scan limits, managed on the Plan page.
Connect With the WeSecureX Team
Have questions about enterprise multi-domain coverage, custom API integrations, or need a guided authorized security assessment? Our engineers respond within 24 hours.
Response Time: Within 24 hours